General
Why You Should Treat Penetration Testing Like a Cyber Drill
Penetration testing can be compared to fire insurance, but it offers much more. Fire insurance compensates you after a disaster; a penetration test acts before one.
Cyberattacks are now a serious threat not only for large enterprises but for businesses of every size. That is why putting security measures in place before an incident happens has become a critical requirement.
In this respect, penetration testing can be compared to fire insurance, but it offers much more. Fire insurance aims to compensate for financial losses after a disaster, whereas a penetration test uncovers vulnerabilities in your systems before an attack takes place. It does not just minimize damage; it prevents the risk from materializing in the first place and gives your business a proactive security shield.
In short, penetration testing goes beyond the classic idea of insurance: it does not only protect you against losses, it aims to keep the attack from ever happening.
What Is Penetration Testing?
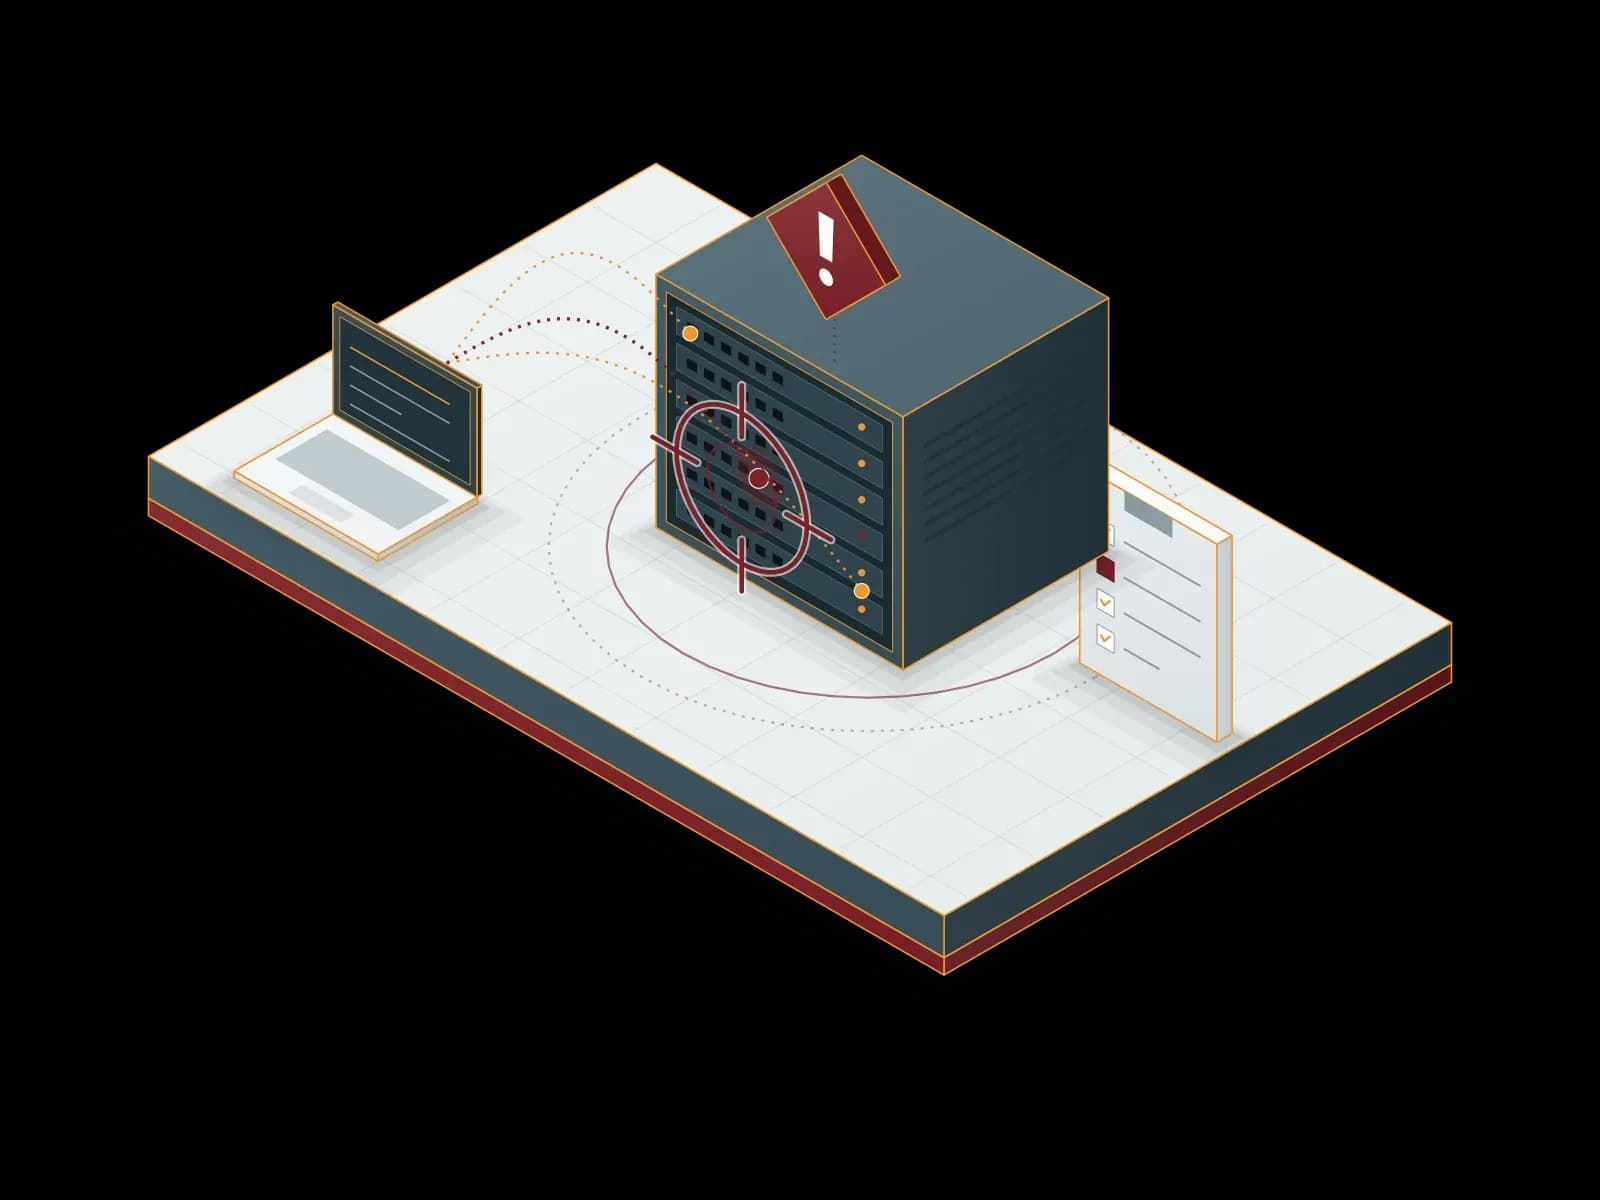
A penetration test (pen test) is a controlled, authorized attack simulation performed to identify the security gaps in a system. The goal is to make sure the organization notices the weak points in its systems before malicious actors can do harm.
The penetration testing service from Synchron Bilişim uses real-world attack methods. Web applications, network architecture, user access, wireless connections and many other components are included in these tests. The tests are carried out by competent, certified cybersecurity specialists.
Passive defenses alone are not enough against current threats. Penetration tests are a critical tool for measuring and improving an organization's cyber resilience.
Detecting security gaps early prevents not only financial losses but also wider impacts such as reputational damage and legal sanctions. Especially under KVKK (Turkey's Personal Data Protection Law) and similar regulations, ensuring cybersecurity proactively is no longer a choice but a legal obligation.
Making sure a fire never starts is worth more than putting one out. Penetration testing protects organizations at exactly this point.
Risks for Organizations That Skip Testing
Organizations that do not have penetration tests performed keep operating without knowing about the vulnerabilities in their systems. From the outside it may look as if there is no problem, but to attackers it means an easy target.
Today, many cyberattacks do not require complex methods. Often a simple configuration error, unpatched software or a weak password can set off a chain of events that leads to a major data leak.
The possible consequences for an organization that is attacked include:
- Leaked customer data
- Reputational damage and broken trust
- Legal liabilities and regulatory fines
- Operational disruption and lost revenue
Penetration testing can prevent these risks to a large extent. Ignoring the risks only buys time; it does not remove the threat.
The Benefits of Penetration Testing
Penetration testing gives organizations many advantages, not only technical but also operational and strategic. The findings clearly show where system security is weak. This makes it possible to identify which risks to prioritize and to direct security investments to the right areas.
Key benefits of penetration testing:
- Early detection of vulnerabilities:
You can take precautions against critical gaps and act before attackers reach them. - Greater cybersecurity awareness:
The test process evaluates not only systems but also user habits, which strengthens the security culture inside the organization. - Readiness for compliance and regulations:
KVKK, ISO 27001 and similar standards recommend regular penetration testing. Test reports play an important role in audits. - Building trust with customers and business partners:
Companies that are proactive about security meet their responsibilities to their stakeholders, which increases brand value.
Penetration testing is a practice that gives you a competitive advantage.
Test Regularly, Not Just Once
Cyber threats do not stand still. Attack techniques keep evolving, software is updated and user mistakes repeat. Penetration testing should therefore not be seen as a one-time solution.
Security gaps can reappear at any time through system updates, infrastructure changes, new users or third-party integrations. The best response to this changing environment is to repeat the tests periodically.
External audits and regulations also require regular testing. In some sectors, for example, a penetration test every six months is a legal requirement.
Cybersecurity is a dynamic process, not a static one. Organizations must keep pace with it and review their security measures continuously.
Penetration Testing Is an Investment, Not a Cost
Organizations often treat penetration testing as an "expense" rather than a budget item, and this is a serious error of perspective. These tests reveal weaknesses in your systems before anyone exploits them. That prevents much bigger costs such as data loss, reputational damage and regulatory fines.
When you look at the damage that follows a cyberattack, the cost of testing is clearly a very small share of the total. And the impact is not only financial: strategic areas such as brand value, customer trust and operational continuity are directly affected too.
A penetration test is like the answer to this question:
"Do you really trust your systems, or do you only feel safe because you have not been attacked yet?"
To answer this question clearly at an organizational level, you need concrete data based on test results.
In short, a penetration test:
- Is a long-term security investment, not a one-off expense.
- Measures how ready you are for potential attacks.
- Protects your organization from risks and turns security awareness into part of your corporate culture.
Fire insurance steps in when disaster strikes. A penetration test works to keep the disaster from ever happening. This difference is too critical to ignore.
A Security Solution Tailored to Your Organization: Penetration Testing with Synchron Bilişim
Synchron Bilişim offers a comprehensive penetration testing service so that organizations can assess their cybersecurity level with concrete data. Our expert, certified cybersecurity team runs the tests with scenarios that fit the organization's current setup.
As part of the test:
- System and application vulnerabilities are identified
- Security weaknesses are detailed in technical reports
- Remediation steps are presented clearly and in an actionable way
Every organization has different security needs. Penetration tests are therefore customized to the organization's infrastructure and sector-specific risk profile. At the end of the process, we share not only the vulnerabilities but also the prioritized actions you need to take against them.
By working with Synchron Bilişim:
- You are prepared for real attack techniques.
- You evaluate your system security through an outside perspective.
- You comply with legal and sector-specific regulations.
The most effective defense in cybersecurity starts with testing your own systems from an impartial, expert perspective.
For detailed information about our services, fill in the form on our contact page and share your details with us. One of our specialists will call you shortly.
About the author
Synchron