Cyber Security
Who Controls Your Active Directory? The Cost of an Unmanaged AD to Your Company
An unmanaged Active Directory quietly costs your company through open accounts, excessive permissions and downtime risk. We cover the warning signs and 5 core practices.
- Author
- Synchron
- Category
- Cyber Security
- Published on
- Updated on
6 min read
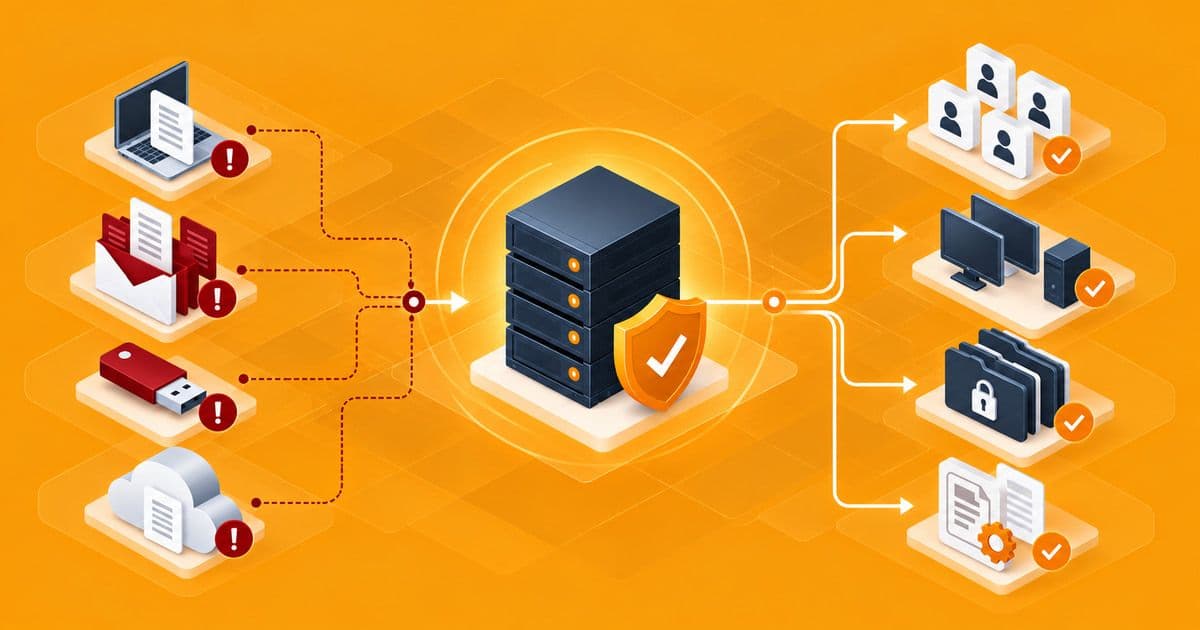
The user account of an employee who left the company six months ago is still active. VPN access is still there, and the permissions on shared folders have never been removed. Nobody did this on purpose; Active Directory management simply has not been anyone's priority for a long time.
This scenario is more common in companies than you might think. Active Directory is configured properly on the day it is set up, but over the years the users, groups and policies added to it turn it into a complex structure. In this article, we look at the real cost of an unmanaged AD to your company and at the ways to fix it.
Why Is Active Directory So Critical?
Active Directory is your company's identity infrastructure. It decides who can sign in to which computer, which files they can access, how they use email and how often they change their password.
For this reason, a weakness in AD affects not a single system but the whole company. For an attacker, a compromised administrator account is the key to the entire network.
The problem is that AD issues are usually silent. As long as the system keeps working, nobody questions who has which permissions. Gaps often come to light during a security incident, an audit or a critical outage.
5 Hidden Costs of an Unmanaged AD
1. Old accounts left open
Accounts of former employees that were never disabled are the doors most open to misuse. Because nobody uses them, suspicious activity on these accounts usually goes unnoticed.
2. Excessive permissions
Permissions granted with a "let's make them an admin for now" attitude become permanent over time. It is common to find far more accounts in the Domain Admins group than there should be.
3. Stale computer and service objects
Unused computer accounts and service accounts whose passwords have not changed for years both create security risks and make the structure hard to read.
4. Scattered Group Policy Objects (GPOs)
Conflicting group policies, created by unknown people for unknown reasons, mean slow sign-ins, unexpected settings and faults that take hours to resolve.
5. Knowledge tied to one person
In companies where only one person knows how the AD structure was built, even the simplest change becomes risky when that person leaves or goes on leave. Missing documentation is an invisible but high cost.
The common result of these five problems is the risk of downtime. A serious AD failure means employees cannot sign in or reach their files and email. In other words, the cost of an unmanaged AD is not only security; it is direct business loss.
How Can You Tell Your AD Is Not Being Managed?
If you cannot give a clear answer to even one of the questions below, it is time to review your Active Directory structure:
- How many active user accounts do you have right now, and does this number match your headcount?
- Who is in the Domain Admins group, and why?
- When were unused accounts last cleaned up?
- Is there a list of your group policies with descriptions?
- When did you last test your AD backup?
The answers to these questions can often be found by running a few reports. But if nobody is responsible for running these reports regularly, interpreting them and taking action, the same problems come back bigger every year.
5 Core Practices for Healthy Active Directory Management
1. Standardize onboarding and offboarding
Set up a clear process between human resources and IT. The account of a departing employee should be disabled and their permissions removed on the same day. New employees should get predefined groups that match their role, rather than a copy of another user's permissions. Copied permissions are the most common source of unnecessary access.
2. Apply the principle of least privilege
Give each user only the permissions they need to do their job. Use dedicated administrator accounts for admin tasks, separate from the account used every day. That way, an account compromised through email or web browsing cannot reach administrator rights directly.
3. Clean up regularly
Periodically report on, review and disable user and computer accounts that have not signed in for a set period.
4. Simplify and document group policies
Record the purpose, scope and owner of each GPO. Remove unused or conflicting policies. At the same time, check that your password and account lockout policies match your current security needs.
5. Monitor and back up
Monitor changes to critical group memberships. Ensure redundancy with more than one domain controller, and regularly test that your AD backup can be restored.
An AD that has a backup but has never had a restore test may not provide the expected protection in a crisis. Deciding in advance who does what in a disaster scenario shortens recovery time considerably.
What Does a Managed Service Model Bring?
A managed service model turns AD maintenance into scheduled work and takes the load off your in-house team. Active Directory maintenance is not a one-off project but continuous work. Yet in most companies the IT team is busy with daily support requests, so this work keeps getting postponed.
In a managed service model, regular checks, clean-up, reporting and documentation of AD are carried out on a schedule. Your in-house team can focus on daily operations and business priorities.
The process usually starts with a comprehensive health check. This check reviews user and computer accounts, privileged groups, password policies, group policies, the state of the domain controllers and replication health. The findings are prioritized and fixed in a planned way without disrupting your business processes.
Regular maintenance follows: periodic clean-up, recording of changes, monthly reporting and up-to-date documentation. Your AD structure then rests not on one person's memory but on a documented, sustainable setup.
Conclusion
Active Directory is one of your company's least visible but most critical systems. When it is not managed, its risks grow silently; with regular maintenance, it improves both security and day-to-day productivity.
At Synchron, we analyze and clean up your Active Directory structure and take over its regular maintenance with a managed service model. Contact us to assess the current state of your AD together.
About the author
Synchron