

Do You Have to Pay the Ransom? 5 Critical Decisions During a Ransomware Attack
The first-hour decisions in a ransomware attack determine the damage. From isolation to the ransom decision, learn 5 critical steps to protect your business.
Posts by this author
The first-hour decisions in a ransomware attack determine the damage. From isolation to the ransom decision, learn 5 critical steps to protect your business.
Moving from a physical server to a VPS removes hardware risk, scales resources, and provides automatic backups and predictable costs. Review the 5 advantages.
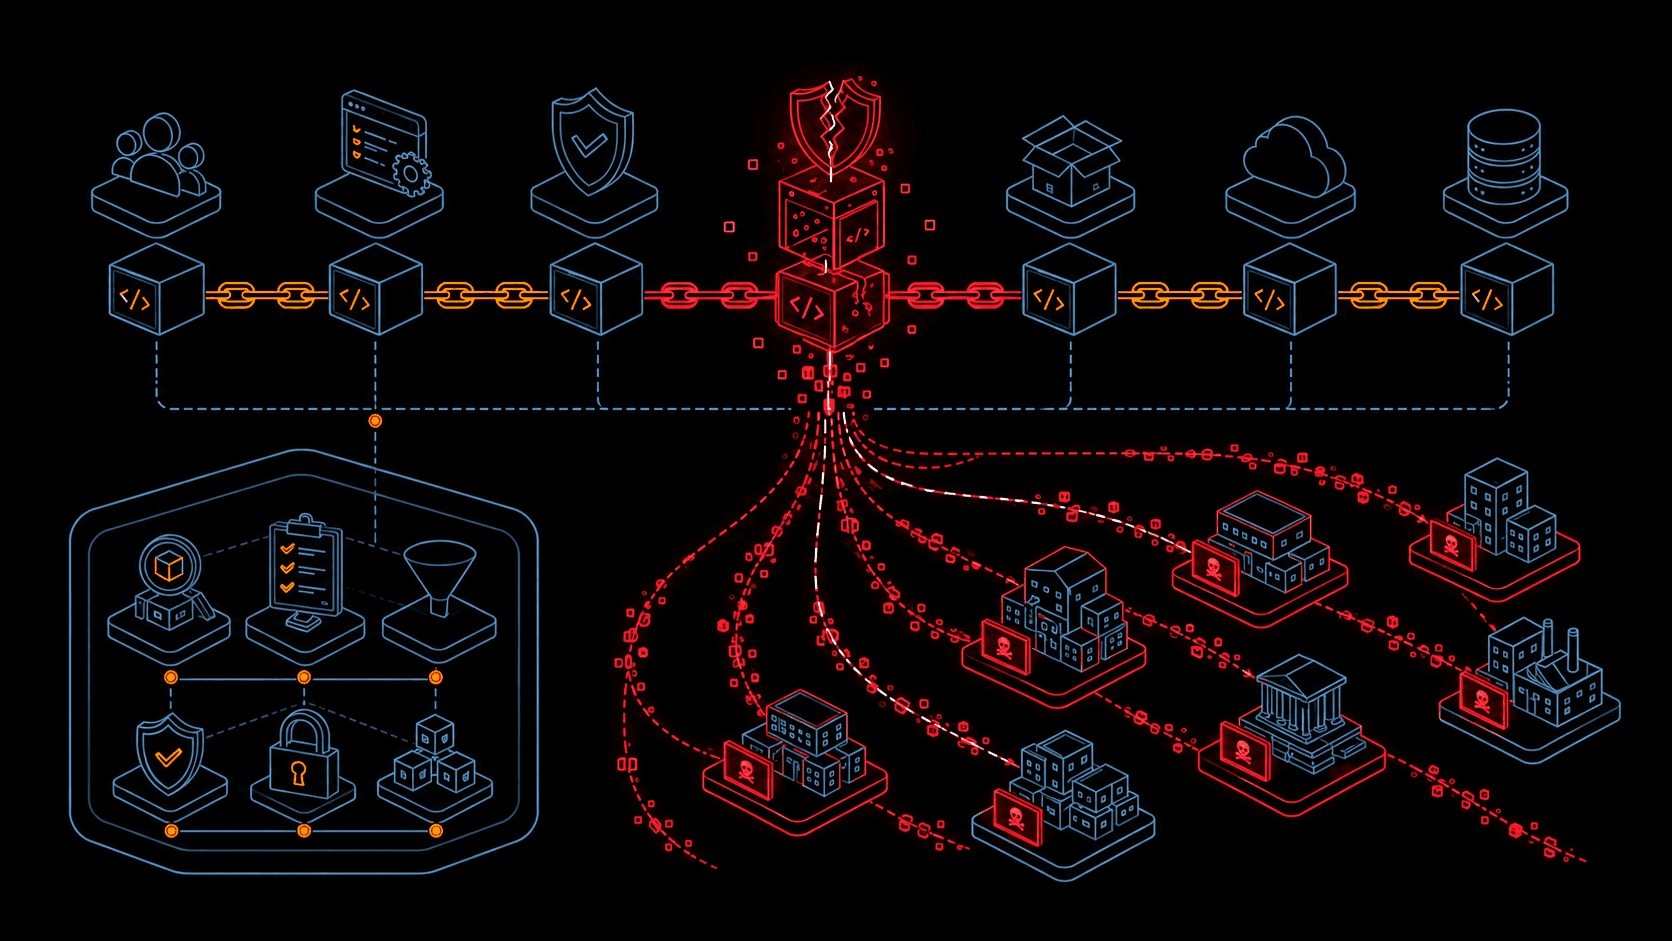
Supply chain attacks get into your organization through the suppliers you trust. Learn how they work and 4 measures that reduce third-party risk for your business.
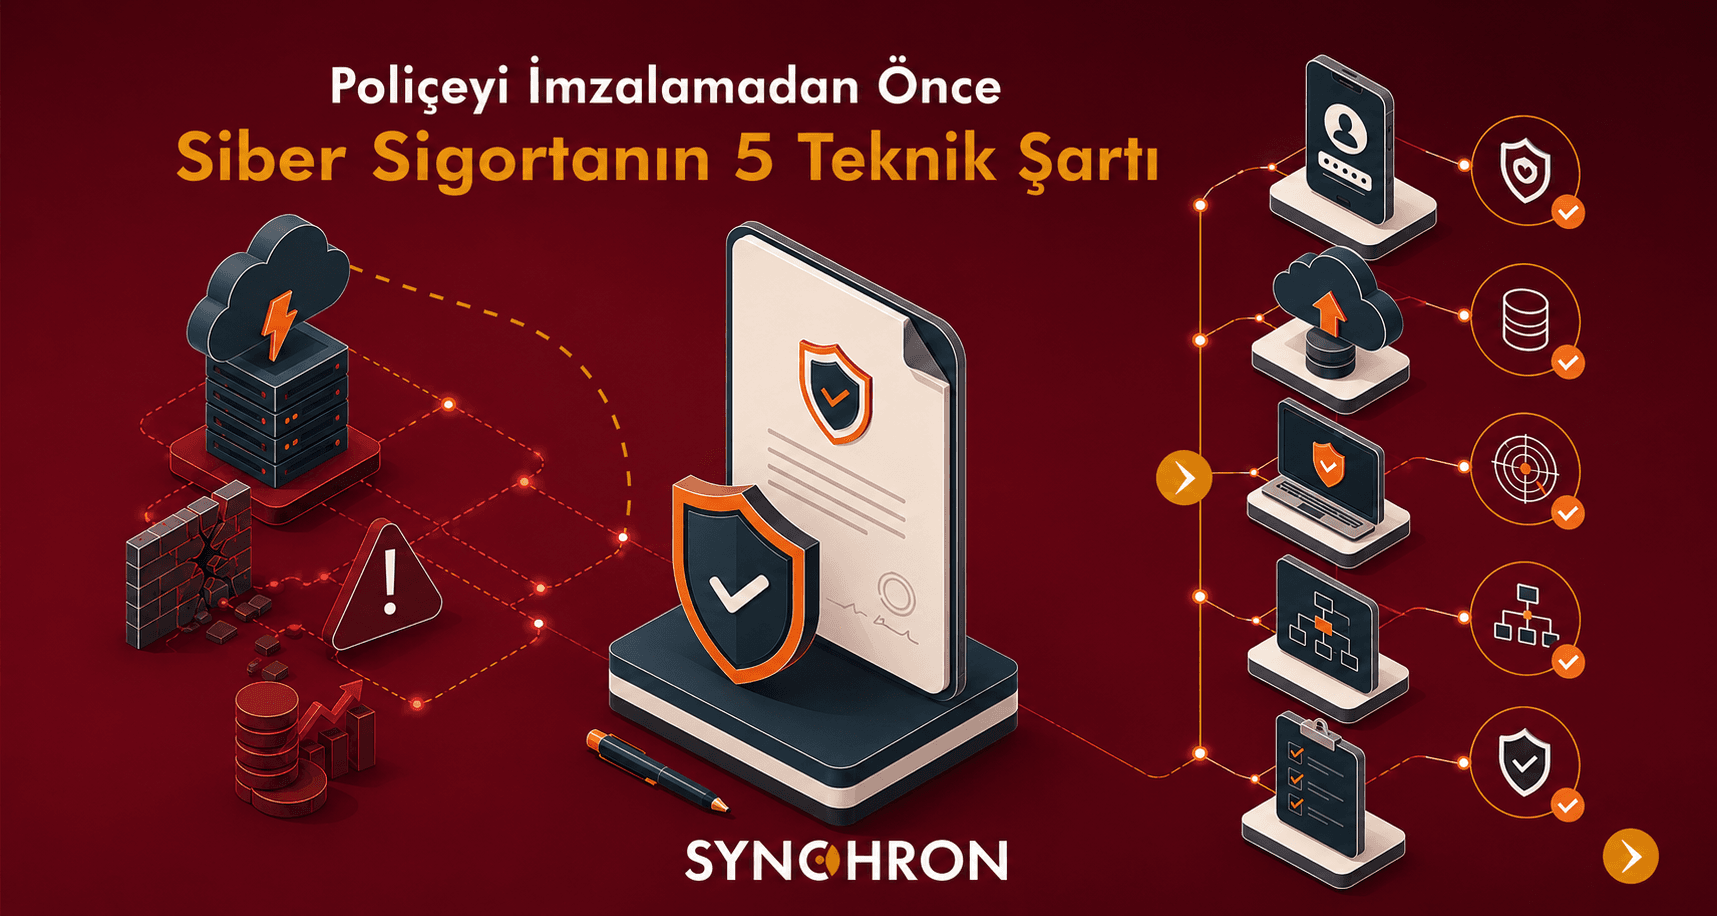
Before you sign a cyber insurance policy, check the 5 technical requirements insurers look for: MFA, EDR/MDR, isolated backups, an incident response plan and central logging.
What is post-quantum cryptography, and what do the NIST standards say? A 4-step preparation plan and practical recommendations for SMEs against the quantum threat.
Deepfake fraud uses AI-cloned voices and video to exploit employees' trust. Learn how these attacks work and 5 measures that protect your organization.
When does IT outsourcing pay off for small, medium and large companies? Review the balance of cost, expertise and 24/7 support in managed IT services.
AI data security is critical for companies, especially for KVKK (Turkish data protection law) compliance. We cover the main risks and 7 concrete measures you can take.
Discover 10 practical cloud cost optimization methods that help you identify unnecessary licenses and idle resources and lower your cloud bills.
Backup testing is skipped for a few typical reasons. For IT teams under time pressure, testing backups usually falls to the bottom of the priority list.
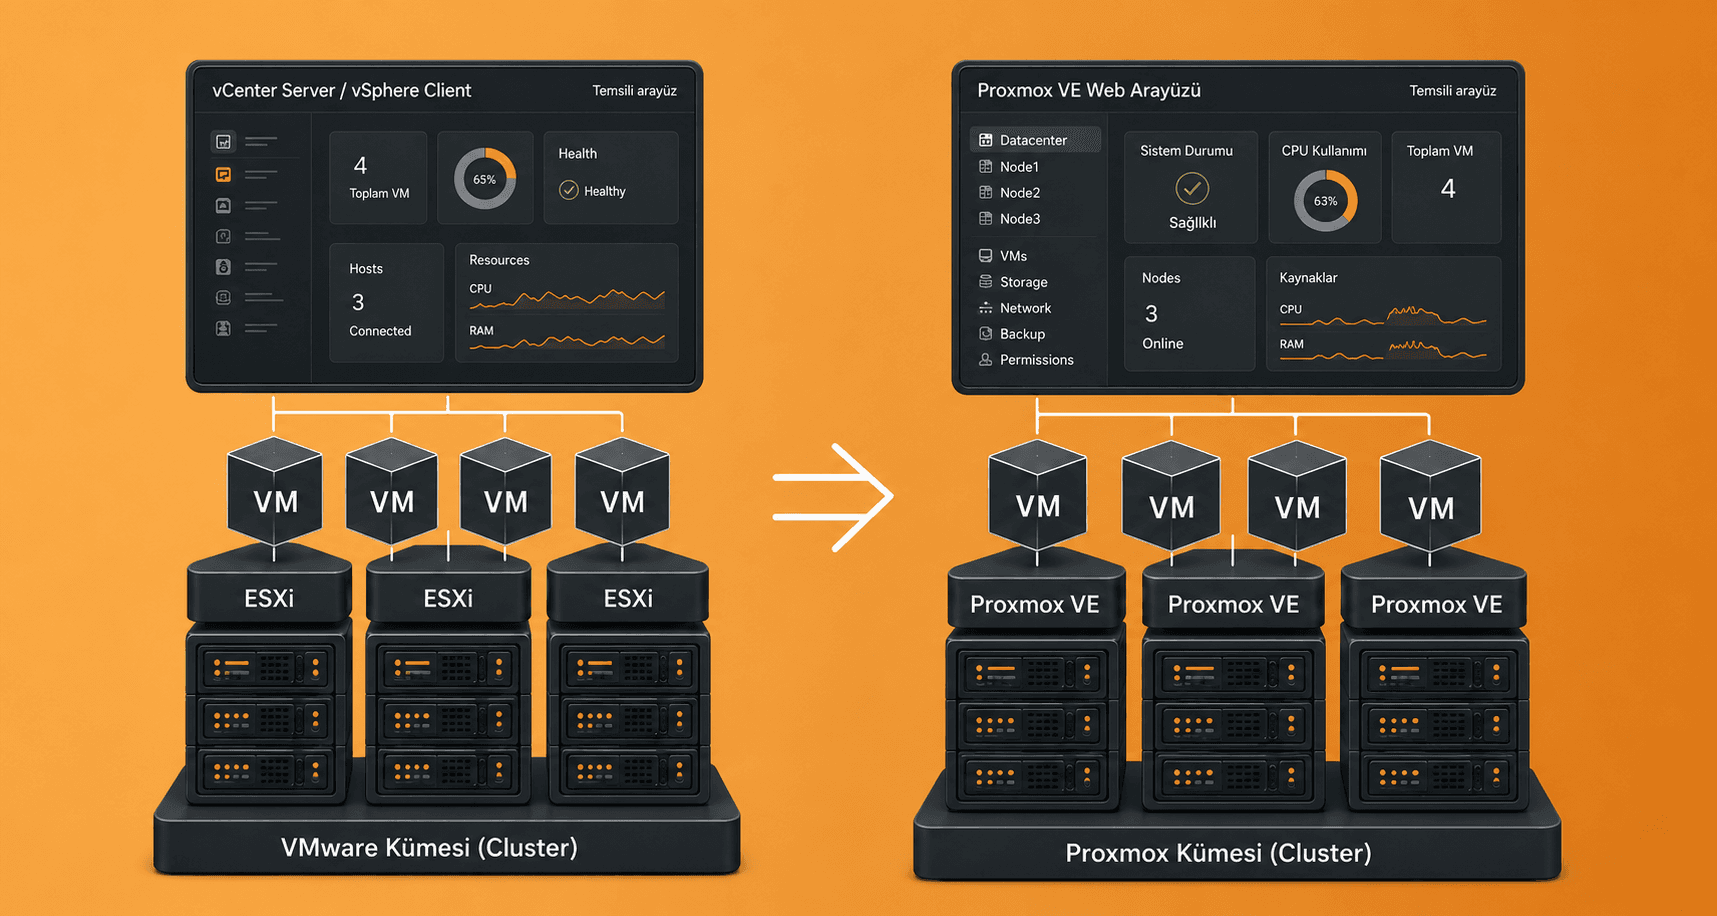
After Broadcom acquired VMware in 2023, the picture changed fast. Perpetual licenses were discontinued and everything moved to a subscription model.
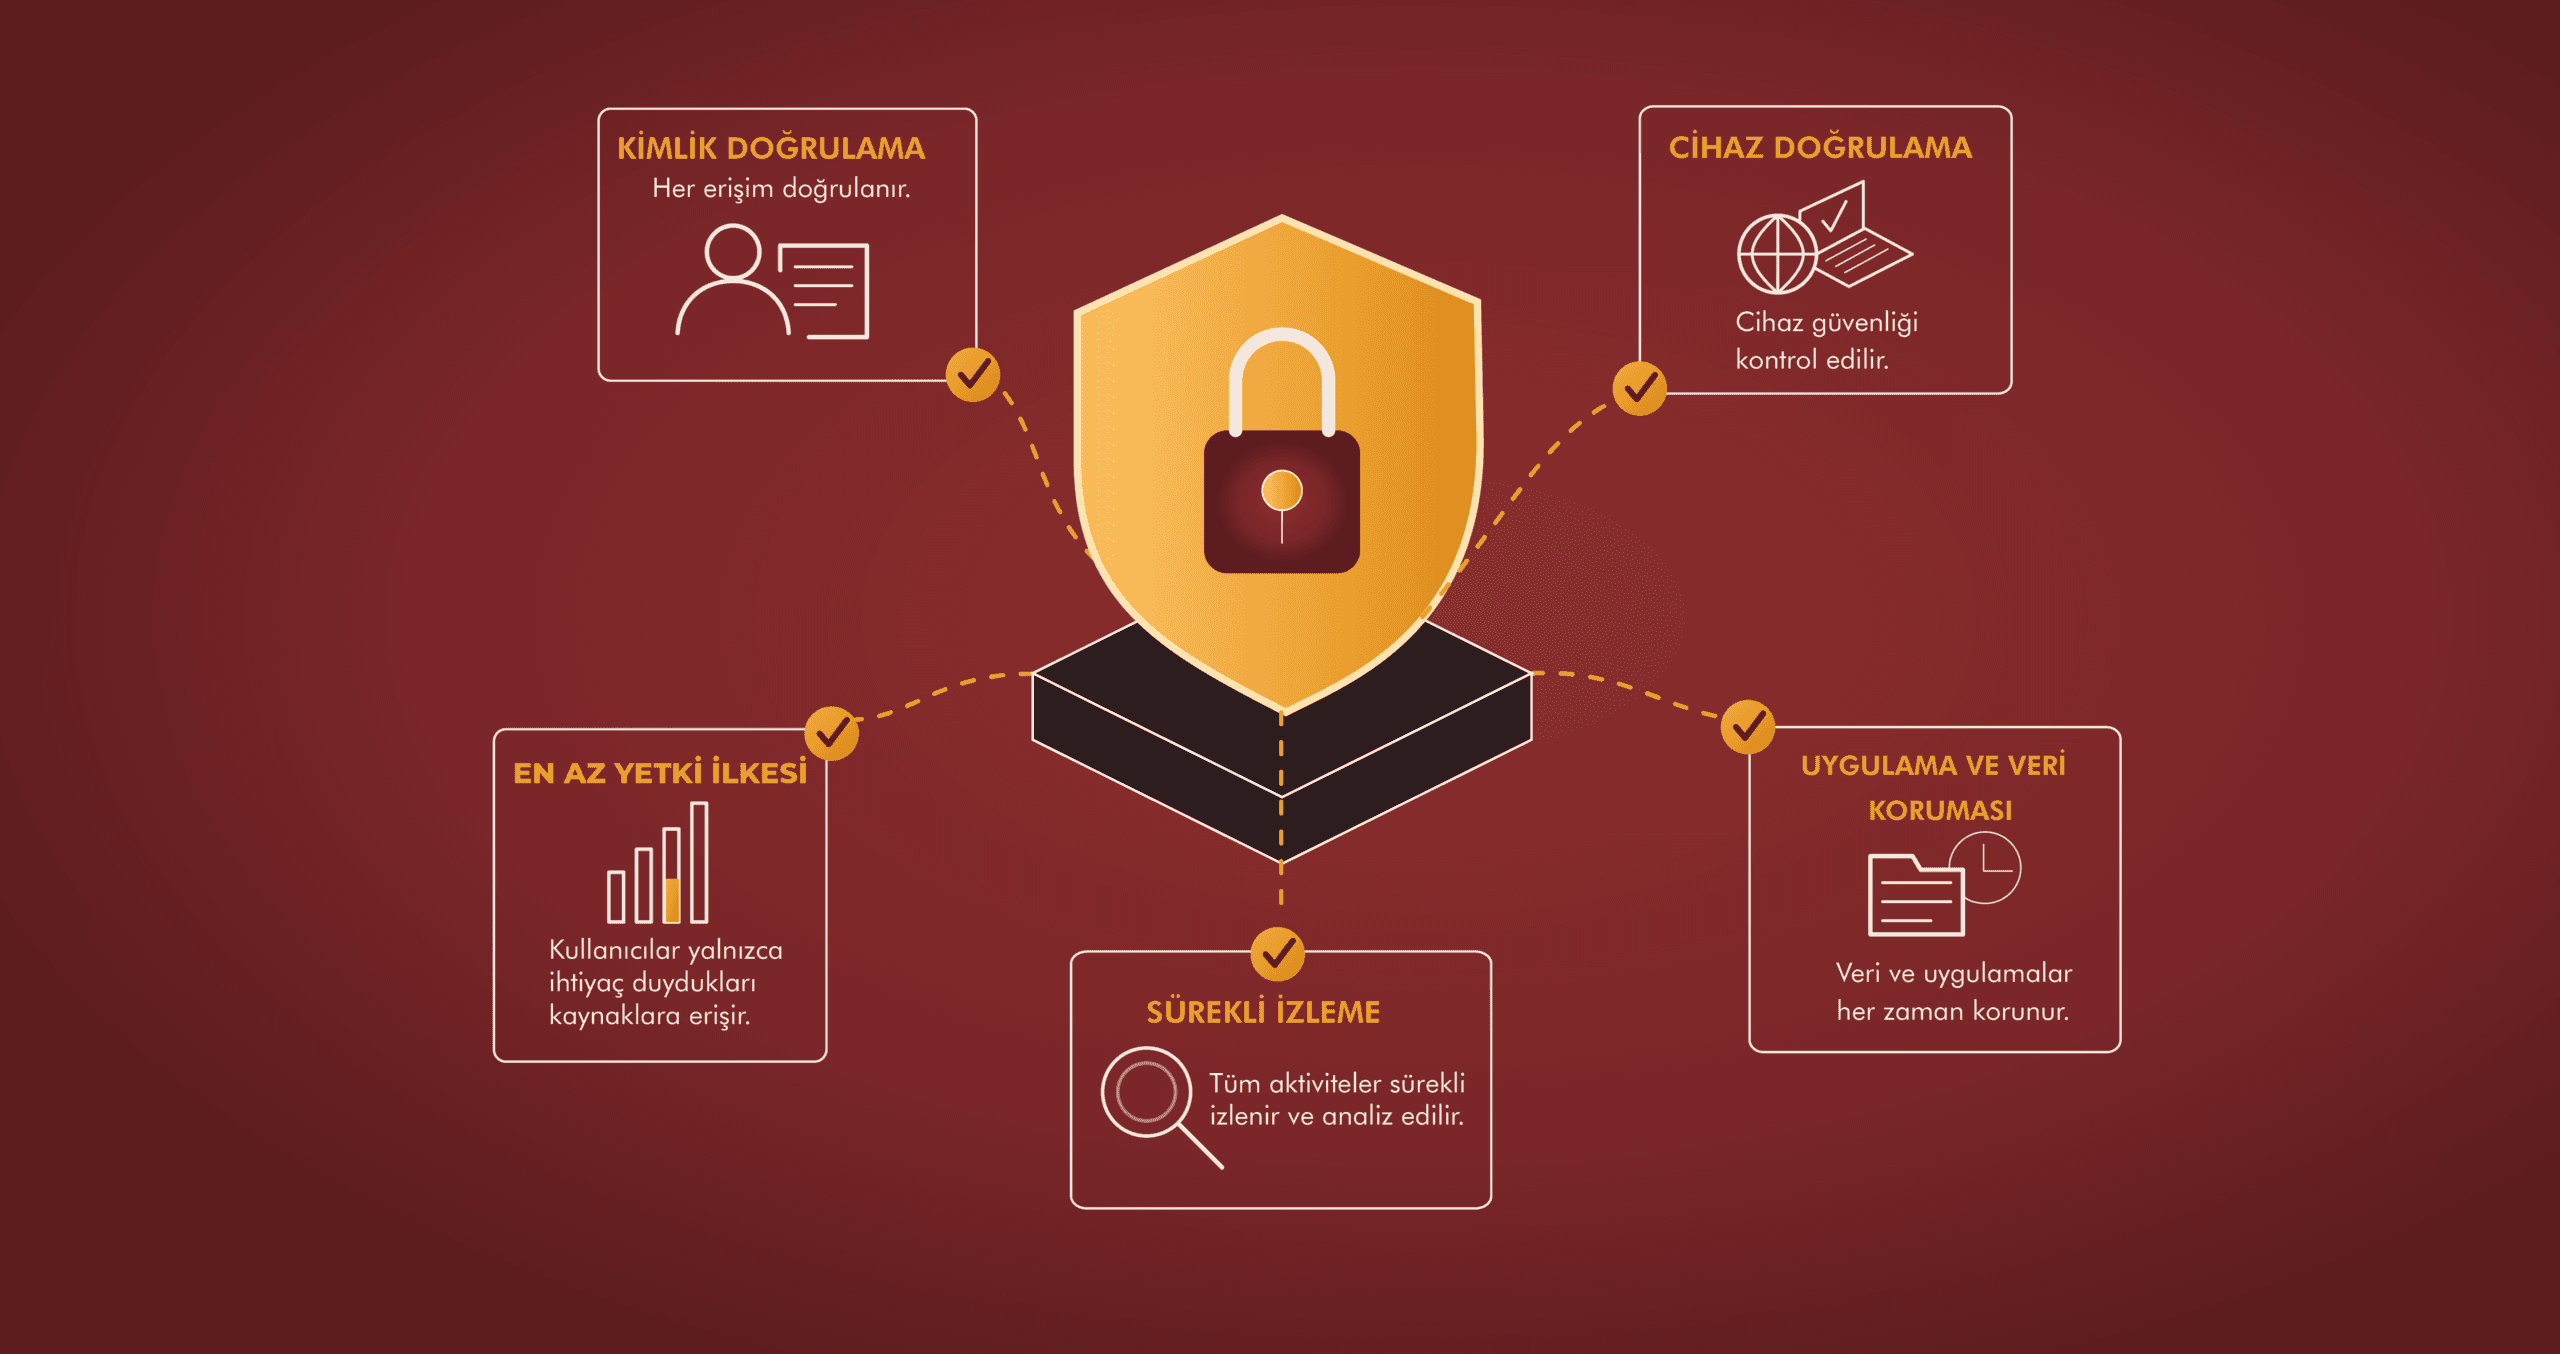
Corporate security was once based on one idea: if you got into the company network, you were trusted. Inside the firewall, there was no problem. That era is over.